How Encryption Actually Keeps Your Data Safe
Encryption is one of those technologies most people use every day without thinking about it. It helps protect messages, passwords, financial transactions, stored files, and information moving between devices and websites. You’ll often see phrases such as “encrypted connection” or “end-to-end encryption” presented as signs that a service is secure.
By Colette Hall on October 3, 2026
Getty Images
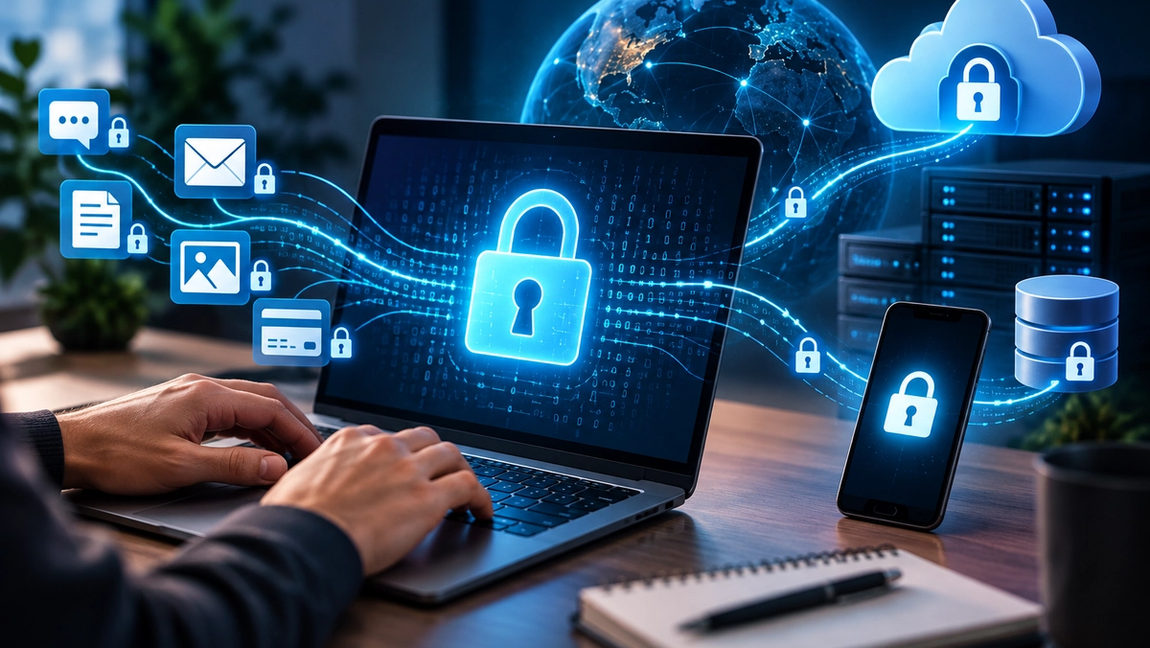
Encryption is one of those technologies most people use every day without thinking about it. It helps protect messages, passwords, financial transactions, stored files, and information moving between devices and websites. You’ll often see phrases such as “encrypted connection” or “end-to-end encryption” presented as signs that a service is secure. But encryption isn’t magic, and it doesn’t automatically protect you from every digital threat. Its main job is surprisingly straightforward: turn readable information into something that can’t easily be understood by someone who isn’t supposed to see it.
Encryption turns readable data into unreadable data
Imagine writing a private message and then transforming every part of it according to an extremely complicated secret system. Anyone who intercepts the transformed version sees information that appears meaningless. Someone with the correct key, however, can reverse the process and recover the original message. Modern encryption follows this basic principle, although the actual mathematics is far more sophisticated. The readable information is often called plaintext, while its encrypted form is called ciphertext. An encryption algorithm performs the transformation using a cryptographic key. Without the appropriate key, recovering the original information should be computationally impractical when strong, properly implemented modern encryption is used. This is why encryption is useful even when attackers manage to obtain data. Stealing an encrypted database, for example, is different from stealing the same information stored in readable form. Encryption doesn’t necessarily prevent someone from accessing or copying the data, but it can prevent that person from making practical use of what they obtained.
Encryption protects data while it moves and while it is stored
Your information generally needs protection in two situations: when it is traveling somewhere and when it is sitting on a device or server. Encryption in transit protects information moving across networks. When you visit a website using HTTPS, for example, encryption helps protect the communication between your browser and the website’s server from being read or altered by someone intercepting the connection. Encryption at rest protects stored information, such as files on a phone, computer, hard drive, or server. Modern phones and computers commonly offer device encryption that can make stored data significantly harder to access without the correct password, PIN, or other authentication. These protections solve different problems, which is why a service may use several forms of encryption simultaneously. A document could be encrypted while stored on a server, encrypted again while traveling across the internet, and protected by additional security controls determining who is allowed to access it.
End-to-end encryption provides an additional layer of privacy
End-to-end encryption is especially important for private communication. In an end-to-end encrypted system, a message is encrypted on the sender’s device and designed to be decrypted only by the intended recipient’s device. The service carrying the message generally shouldn’t possess the keys required to read its contents. Imagine putting a letter inside a locked box before giving it to a delivery company. The company can transport the box, but only the recipient has the key needed to open it. This differs from systems where data is encrypted while traveling to a company’s server but can be decrypted and processed there. Both approaches can use encryption, but they provide different levels and types of protection. End-to-end encryption can significantly reduce who has technical access to message contents, but it doesn’t make communication completely anonymous. Services may still retain certain metadata, depending on how they’re designed, and recipients can still copy, photograph, forward, or otherwise share information after receiving it.
Encryption is powerful, but it can’t protect everything
Strong encryption is an essential security tool, but it works best as one part of a larger security system. If someone steals your password through a convincing phishing attack and logs into your account normally, encryption may not prevent them from seeing information that the account is authorized to access. Similarly, if your unlocked phone is taken while you’re using it, device encryption offers less protection because the device may already have access to the necessary keys. Malware running on a device can also potentially capture information before it is encrypted or after it has been decrypted. This is why good digital security combines encryption with strong passwords, multi-factor authentication, software updates, careful permission management, backups, and protection against phishing. Encryption solves a specific and extremely important problem: it makes information unreadable to parties that don’t have the appropriate cryptographic access. You don’t need to understand the mathematics behind it to benefit from it. Every time an encrypted connection protects a transaction, an encrypted device protects stored files, or an end-to-end encrypted service protects a conversation, complex cryptography is quietly helping keep ordinary digital life private.